
MyQ X synchronizes users from Google Workspace using Google's Secure LDAP service, which provides read-only access to the Google directory over LDAPS. The synchronization imports user accounts and group memberships and maps directory attributes to MyQ user properties.
Guidance on when to use this source is provided in the Deployment guide. See User Synchronization.
See also: Synchronize Users from LDAP.
Prerequisites
-
Super Admin privileges in Google Workspace.
-
A Google Workspace subscription that supports the Secure LDAP service.
-
The MyQ server must be able to establish outbound LDAPS connections (TCP 636) to Google.
-
Familiarity with which users or groups MyQ should be allowed to access.
Key Considerations
Each MyQ server instance requires its own LDAP client certificate. Google issues a unique certificate per LDAP client. If you run multiple MyQ servers – for example, a Central Server and Site Servers – each must have its own client registered in Google Admin with its own certificate and credentials.
Certificates expire and must be renewed. Google Workspace LDAP client certificates have an expiry date. Plan certificate renewal into your operational calendar. When a certificate expires, synchronization will fail until a new certificate is generated and uploaded to MyQ.
Access permission changes can take up to 24 hours to take effect. When you modify LDAP client access permissions in Google Admin Console, the changes are not immediate. Account for this delay during initial setup and testing – if sync is not returning expected results shortly after a permission change, wait and retry before troubleshooting further.
The client certificate must be in PEM format. MyQ requires the client certificate in PEM format (Base64-encoded, with BEGIN CERTIFICATE headers). If the certificate downloaded from Google Admin is in binary DER format, convert it before uploading to MyQ, for example using OpenSSL: openssl x509 -inform der -in certificate.der -out certificate.pem
Do not protect the private key with a password. MyQ cannot use a password-protected private key. When generating credentials in Google Admin, leave the private key unprotected.
Configure the LDAP Client in Google Admin
This step is performed entirely in the Google Admin Console. It produces the client certificate, private key, and LDAP credentials that MyQ needs to connect.
-
Sign in to the Google Admin Console with a Super Admin account.
-
Go to Apps > LDAP and click Add Client.
-
Enter a name for the client (required) and an optional description. Click Continue.
-
On the LDAP client page, click Access Permissions and configure the following:
Verify user credentials – enables user authentication via MyQ. Set to all users or to specified organizational units.
Read user information – enables MyQ to read user attributes. Set to all users or to specified organizational units, then enable access to:
-
System Attributes
-
Public Custom Attributes
-
Private Custom Attributes
Read group information – allows MyQ to read directory group membership. Set to On.
-
-
Click Add LDAP Client and wait while the client is provisioned and a certificate is generated. This may take a few minutes.
-
Download the generated certificate package. The ZIP file contains:
-
The client certificate (
.crtor.pem) -
The private key (
.key)
Store these files securely. If the certificate is in DER format, convert it to PEM before proceeding.
-
-
Click Continue to Client Details.
-
Click Access Credentials, then click Generate New Credentials. The generated username and password are displayed once only – store them securely before leaving this screen.
-
Return to the LDAP client details page and set the Service Status to ON for everyone. Click Save.
Google Workspace is now configured with MyQ as an LDAP client.
Configure the Authentication Server in MyQ
Go to MyQ > Settings > Authentication Servers and add a new LDAP server for Google Workspace.
|
Setting |
Value |
|---|---|
|
Security |
SSL |
|
Port |
636 |
|
Server |
|
|
User |
The username generated in Google Admin (Step 1) |
|
Password |
The password generated in Google Admin (Step 1) |
|
Client certificate |
Upload the |
|
Private key |
Upload the |
Configure the Synchronization Source
Go to MyQ > Settings > User Synchronization, click +Add, and select Add LDAP source.
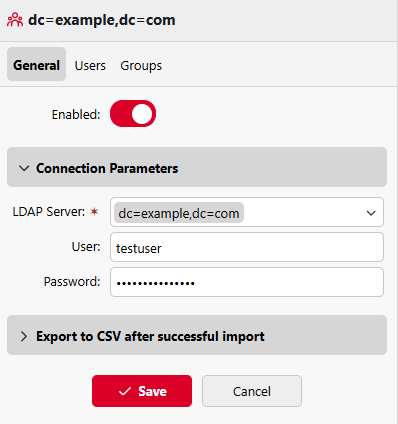
The following covers what is specific to Google Workspace.
Base DN
The Base DN for Google Workspace uses the domain components of your Google Workspace domain. For example, for the domain example.com:
dc=example,dc=com
Default Attribute Mapping
Google Workspace exposes a standard LDAP schema. The following mappings are typical for most Google Workspace directories, but confirm attribute names against your actual directory using the LDAP browser in the General tab.
|
MyQ Property |
Typical Google Workspace Attribute |
|---|---|
|
Username |
|
|
Full name |
|
|
|
|
|
Alias |
(none – configure explicitly if needed) |
|
Personal number |
(none – configure explicitly if needed) |
Run and Schedule Synchronization
To run synchronization immediately, go to MyQ > Settings > User Synchronization, select the source, and click Synchronize now. If configured correctly, synced users and groups appear under MyQ > Users.
To synchronize automatically on a schedule, go to MyQ > Settings > Task Scheduler and configure the User Synchronization task.
Security Considerations
LDAPS Is Mandatory
Google's Secure LDAP service only operates over LDAPS – plain LDAP is not supported. Ensure the MyQ server can reach ldap.google.com on TCP 636 and that no firewall rule blocks outbound connections on that port.
Protect Client Certificates and Credentials
The client certificate, private key, and generated credentials provide read access to your Google directory. Store them securely and limit access to the MyQ server and its administrators. Rotate credentials if they are exposed.
Apply Least Privilege via Access Permissions
In Google Admin, scope the LDAP client's access permissions to only the organizational units MyQ needs to read. Granting access to all users when sync only covers a subset of the organization is unnecessary exposure.